Integration

Use your sign-in provider for iService access

iService connects agent and portal sign-in to your organization’s provider. Administrators manage staff changes and central sign-in policy in that provider. Agent roles control product permissions. Customer contacts cannot use agent login.

Separate identity providers converging through keyed gateways into one access panel

Provider-based access control

Administrators manage staff changes and sign-in policy through the organization’s provider.

iService uses your provider for access. Administrators manage staff changes with central sign-in policy. Agents and portal users sign in through the provider. iService uses the provider for sign-in and product roles for permissions.
A figure arriving at a doorway with a key while a separate mechanism inside sets how far they may go

Agent and portal sign-in

Agent and portal users sign in through the provider while iService roles control agent permissions.

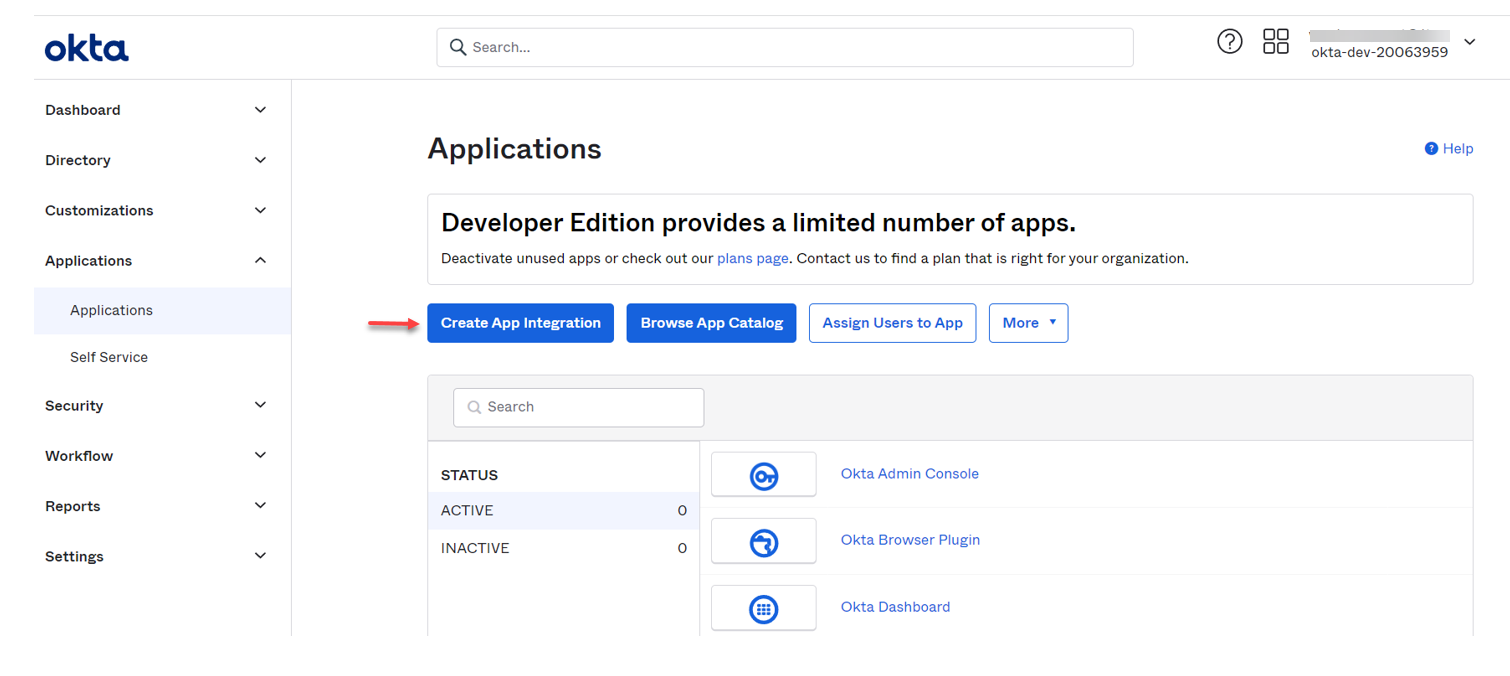
iService Single Sign-On connects agent and portal access to the organization’s provider. For Okta, administrators save the Client ID and domain in iService. Agents select Sign in With Okta. The provider signs in the agent, and iService roles control permissions.

iService configured for single sign-on through an Okta OpenID application

A new agent signs in

A new service agent signs in through the organization’s provider and receives the assigned iService role.

A new agent joins the service team and signs in through the organization’s provider. iService applies the agent role assigned for that work. When staff access changes, administrators manage sign-in access through the provider. The iService role continues to control product permissions.

Sign-in policy and product roles

The provider signs in users, and iService roles control agent access to product work.

iService signs agents in through SSO. Customer contacts cannot use agent login. Agent roles control permissions after sign-in. The provider controls sign-in policy, and iService controls product roles.

Sign-in provider and iService roles

Sign-in policy lives in the provider, and agent permissions live in iService roles.

iService connects staff and portal sign-in to the existing provider. The provider applies sign-in policy. iService roles apply the permissions agents need after sign-in.

Read iService sign-in docs

iService connects agent and portal sign-in to the organization provider while agent roles control permissions.

Read Authentication Docs