Integration

Collect Microsoft 365 email in iService

iService collects service email from Microsoft 365 mailboxes through Microsoft Graph. Each message becomes an interaction that moves to a topic and queue for the assigned agent. Mailbox collection uses Microsoft tenant delegated permissions. Staff sign-in remains a separate configuration.

Microsoft email flowing through a connection into a routed service interaction

Use existing Microsoft 365 mailboxes

Service teams collect customer email from Microsoft 365 mailboxes under their organization’s tenant policy.

iService collects service email from existing Microsoft 365 mailboxes. Mailbox collection stays within the Microsoft tenant model. The service channel uses the tenant permissions and policy the organization administers. Staff sign-in remains separately configured.
A tall stack of past exchanges with the newest bright at the top becoming a work item

Collect mail through Microsoft Graph

Microsoft Graph mail collection uses delegated tenant permissions, and agent sign-in has a separate configuration.

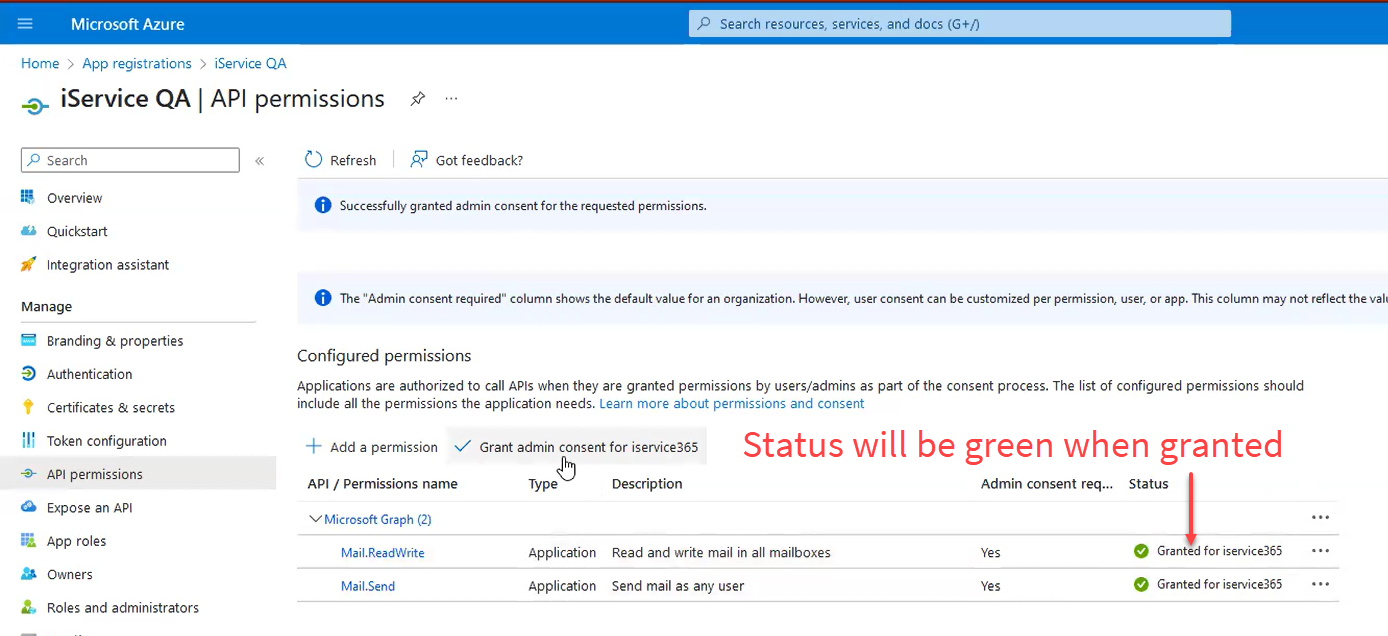
iService uses Microsoft tenant delegated permissions to collect mail through Microsoft Graph. One Graph credential entry serves all Graph mailboxes. Administrators configure Microsoft staff sign-in separately. Mailbox collection and agent sign-in use distinct iService settings.

iService connected to a Microsoft 365 mailbox through the Graph API

Microsoft 365 email becomes service work

A Microsoft 365 customer email becomes an interaction with a topic, queue, and agent response action.

A customer email arrives through Microsoft Graph and iService converts it to an interaction. The interaction moves to a topic and queue. The assigned agent uses an Answer Panel to respond. The original email remains part of the customer-service interaction and workflow.

Microsoft tenant permissions for service email

Microsoft tenant delegated permissions govern iService service-mail collection.

iService uses Microsoft tenant delegated permissions to collect mail through Microsoft Graph. One Graph credential entry serves the Graph mailboxes. The Graph credential and staff sign-in remain separate configurations in iService.

Separate mailbox collection and agent sign-in

Microsoft Graph mailbox collection and agent identity use separate iService configurations.

iService keeps the two setups separate. One Graph credential entry serves Graph mailboxes, and Microsoft staff sign-in has its own configuration. Administrators collect service email through the tenant model and manage agent identity through the sign-in configuration.

Read Microsoft Graph setup docs

iService collects Microsoft 365 email through Microsoft Graph and routes each interaction to an agent queue.

Read Technical Docs